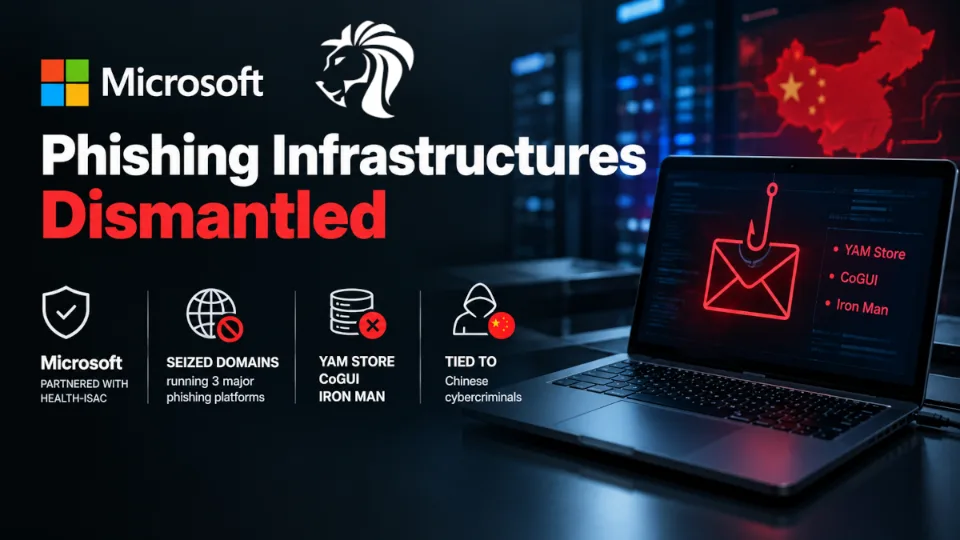
On 14 October 2026, Microsoft's Digital Crimes Unit and Health-ISAC seized and redirected the domains behind three linked criminal services: YAM Store, CoGUI and Iron Man.
The numbers are substantial. Since January 2026, those three services collectively enabled more than one billion malicious messages aimed at over 75,000 organisations worldwide, including more than 750 million directed at Microsoft customers alone. Microsoft has disabled over 20,000 accounts tied to YAM Store and is blocking more than 100,000 domains used for impersonation and fraud.
What makes this case worth studying is not the volume. It is the structure. None of these three services ran phishing campaigns. They supplied them — accounts from one, lure pages from another, infrastructure from a third. This was a takedown aimed at a supply chain rather than at an attacker.
What happened
The legal mechanism
Microsoft and Health-ISAC obtained an order from the US District Court for the Southern District of Florida authorising them to seize and redirect the domains underpinning all three services. Reporting describes it as a temporary restraining order.
This is a civil action, not a criminal prosecution. No one has been arrested. The approach — using court-authorised domain seizure to take infrastructure away from criminals rather than waiting to identify and extradite them — has become the DCU's standard playbook, and it works precisely because the operators are usually beyond reach.
Why a health-sector organisation? Health-ISAC is a global non-profit that helps healthcare organisations share threat intelligence and improve resilience. Its role as co-plaintiff reflects both how heavily the health sector is targeted by credential phishing and the practical value of having an affected-industry body join the filing.
The investigation also drew in Japan's National Police Agency and the Japan Cybercrime Control Center (JC3), with support from TRM Labs, Proofpoint and Resecurity.
The three services
Microsoft tracks YAM Store as Storm-3119, and the associated phishing kits — CoGUI, Haozi (also called Phoenix) and Iron Man System — collectively as Storm-2990.
Service | What it sold |
|---|---|
YAM Store | A marketplace for fraudulently obtained or compromised Microsoft and Google accounts, licences, storage, cloud environments and domains |
CoGUI | A phishing kit: ready-made fake websites and deceptive messages impersonating businesses, banks and government agencies |
Iron Man | Phishing-kit-as-a-service with over 2,300 pre-built lure pages, sold by subscription |
Investigators found similarities between the infrastructure of all three, indicating close collaboration between their developers or shared development origins.
The handover from CoGUI to Iron Man
CoGUI has a documented history. Proofpoint identified it in late 2024, running email campaigns consistently aimed at Japan. Microsoft reports it was used heavily against victims in both Japan and the United States. Further investigation found more than 17,000 domains across three related kits — CoGUI, CoAceV and CoFish_Ws.
Then the market moved. Iron Man began appearing in YAM Store advertising in June 2026, and by mid-2026 criminals were shifting to it in preference to CoGUI. Iron Man's templates impersonate postal companies, traffic-fine offices, tax agencies, banks, retailers, delivery services and telecoms, tailored for Australia, Japan, India and dozens of other countries.
That transition is the most telling detail in the whole case. A criminal service was displaced by a better-featured competitor inside its own marketplace, in a matter of months. This is a functioning market, with product cycles.
A note on attribution
Your framing matters here. Microsoft describes this as a Chinese-language cybercrime marketplace — a description of the language the operators and customers do business in. That is not the same as attributing the operation to the Chinese state, and Microsoft makes no such claim. It is financially motivated crime, not espionage. Worth keeping precise.
How the operation works
The supply chain model
A convincing phishing campaign needs several things that are awkward to produce yourself: somewhere to host the fake page, a sending identity with enough reputation to get past filters, a convincing replica of a real brand, and a way to convert stolen credentials into money.
This network split those jobs apart. YAM Store handled procurement — accounts and infrastructure. CoGUI and Iron Man handled presentation — the lure pages and messages. A customer with modest skills could assemble a credible campaign by buying components.
That division is what makes it a supply chain, and it is why Microsoft went after the suppliers rather than the campaigns.
The expired-domain trick
One technique deserves particular attention because the defence is entirely in the victim's hands.
YAM Store's operators bought internet domains that real organisations had allowed to expire — including domains previously used by nonprofits and educational institutions — and rebuilt websites on them to look like legitimate platforms. Those sites were then used to steal Microsoft 365 credentials, which were sold back on YAM Store.
The value here is inherited reputation. A domain with years of legitimate history, existing inbound links and a clean security record sails past filters that would stop a freshly registered one. Nonprofits and schools are attractive targets because they churn through campaign and project domains and rarely have a process for retiring them safely.
Device-code phishing
Microsoft reports that many of the 750 million messages aimed at Microsoft 365 customers used device-code phishing to obtain authentication tokens.
In plain terms: the attacker starts a legitimate sign-in on a device, which generates a short code. The victim is persuaded — often by a message that looks like IT support or a meeting invitation — to enter that code on Microsoft's real login page. Everything the victim sees is genuine. When they approve, the token is issued to the attacker's session.
Why this matters: the victim never types a password into a fake site, so credential-phishing training doesn't catch it. Because a valid sign-in is completed, many MFA configurations are satisfied. And the attacker ends up with a token rather than a password, which can keep working after a password reset.
Evading analysis
In February 2026, CoGUI introduced a decoy technique that redirected automated analysis sandboxes to harmless domains such as www.a.com, so that security tooling examining the link saw something innocuous while real victims were sent to the phishing page. Kits of this class routinely filter by IP range, user agent and geography for the same reason.
Why it matters
Phishing-as-a-service has lowered the skill floor to near zero. A subscription buys 2,300 ready-made lure pages across dozens of countries. The customer needs no development ability and no infrastructure of their own.
Attacking suppliers scales better than attacking campaigns. Taking down one phishing site removes one phishing site. Taking down the shop that sold the accounts, the kits and the domains degrades every customer at once. This is the strategic logic of the operation.
Targeting is global and localised at the same time. Templates tailored for Australia, Japan and India, impersonating local tax offices and postal services, mean the generic advice about "poor English and odd formatting" is obsolete. These lures are produced natively for each market.
Device-code phishing breaks common assumptions. Organisations that consider themselves protected because they have MFA enabled should look specifically at whether device-code flow is restricted in their tenant.
And it will come back. Microsoft itself acknowledges these three are only part of a larger criminal network. Analysts expect the operators to migrate to alternative marketplaces or rebuild under new names within weeks. A useful signal to watch is whether YAM Store, CoGUI or Iron Man reappear under fresh domains or sales identities.
Who is affected
Microsoft 365 and Google Workspace customers, whose accounts were the product being traded.
Healthcare organisations, enough so that their sector ISAC joined the lawsuit.
Organisations in Japan, the United States, Australia and India especially, where the kits had dedicated localised templates.
Nonprofits and educational institutions, in an unusual way: not only as phishing targets but as the unwitting source of domains that were allowed to lapse and then weaponised against others.
Brands whose identity is impersonated — postal services, tax agencies, banks, telecoms, retailers — which bear reputational damage from scams they have no way to prevent.
Any organisation that relies on email filtering alone, which is the control these services were specifically engineered to defeat.
What attackers can do with these services
Buy working accounts outright, skipping the compromise stage entirely.
Send from domains with legitimate history, inheriting reputation that defeats filtering.
Impersonate local institutions convincingly, in the right language, with the right branding, for the right country.
Harvest authentication tokens rather than passwords, maintaining access through password resets.
Evade automated analysis, so the link looks clean when a sandbox opens it.
Scale to a billion messages without writing a line of code.
What organisations should do
Identity
Restrict or block the device-code authentication flow in Entra ID unless you have a specific need for it. This is the single highest-value action from this report, and most organisations do not need the flow enabled for general users.
Deploy phishing-resistant MFA — FIDO2 keys or certificate-based authentication — which defeats both credential theft and code-relay techniques.
Enable token protection and continuous access evaluation, so a stolen token cannot simply be replayed from another device or location.
Revoke sessions, not just passwords, whenever you suspect compromise. A password reset alone leaves an issued token working.
Domains — including the ones you stopped using
Inventory every domain your organisation has ever registered, including campaign, event, project and legacy brand domains.
Do not let domains quietly expire. Either renew indefinitely or retire them deliberately: remove DNS records, revoke certificates, and ideally hold the registration rather than releasing it. The cost of a renewal is trivial against the cost of your former domain being used to phish your own community.
Monitor for lookalike domain registrations against your brand, and have a takedown route ready.
Email and web defence
Enforce DMARC at enforcement level, with SPF and DKIM aligned, so impersonation of your own domain fails.
Do not rely solely on link reputation. These kits are built to show sandboxes something harmless. Detonation in a realistic environment, and inspection at click time, both help.
Watch for sign-ins from newly seen infrastructure following a message campaign, rather than trying to catch the message itself.
People
Train specifically on device-code and code-entry scams, which look nothing like classic phishing. The rule is simple and worth stating plainly: never enter a code that someone else gave you, no matter how legitimate the page you are entering it into appears.
Retire the "spot the bad grammar" advice. With 2,300 localised templates in circulation, lures in your users' own language impersonating their own tax office are routine.
Final thoughts
The instructive thing about this takedown is who was targeted. Microsoft did not go after the criminals sending the billion messages. It went after the three businesses that sold them accounts, templates and domains — and did it with a civil court order rather than an indictment, because the sellers are not reachable by arrest.
The lesson: modern phishing is a supply chain, and most defences are still built for a lone attacker. Behind a single convincing fake login page sits a marketplace that sold the domain, a kit vendor that supplied the template, and a broker that will buy the stolen credentials afterwards. Each layer is a separate business with separate customers.
The second lesson is smaller and more actionable. A meaningful share of this operation ran on domains that legitimate organisations stopped paying for. Nonprofits and universities let project domains lapse, criminals bought them, and years of accumulated trust were turned against the public. Domain lifecycle management is not glamorous, and it is not usually anyone's job. In this case it was a national-scale attack surface.
So two questions to take away: is device-code sign-in still enabled in your tenant, and do you know what happened to every domain your organisation has ever owned?